
On the Cloud
On your Server
Get in touch
Auth done right, once.
Open-source auth and user management for consumer and frontline identity. Start free with Passkeys, WhatsApp and SMS OTP, SAML SSO and RBAC. Run it on our cloud, in your VPC, or on your own hardware.
- ISO 27001
- SOC 2 Type II
- Open source
- Self-hostable



Why teams switch to Authgear
Most CIAM vendors charge extra for SSO, hold your user data hostage, and re-price you at renewal. Here is what we do instead.

No feature gates
Every plan, including Free, ships with passkeys, adaptive MFA, SAML SSO, Active Directory login, and RBAC. Only a custom SMS gateway and advanced security cost more. You never buy a tier to unlock a login method.

Runs where your data has to live
One open-source platform, on Authgear Cloud, in your VPC, or on your own hardware. Regulated workloads stay in-region, on infrastructure you control.

An exit you can actually take
Export every user, password hashes included, whenever you want. Authgear is open source and OIDC-compliant, so leaving is a decision, not a rebuild. We would rather you stay because it works.

A vendor that will still be here
Bootstrapped and profitable, not raising toward an exit. Built by Skymakers, which has served enterprises worldwide for over ten years. No acquisition notice, no sunset date, no forced migration.
Why enterprises trust Authgear
Transit, healthcare, property, and global food service. Teams that answer to auditors, run at scale, and cannot afford to migrate twice.
Phone Number OTP Revolutionizes Fitness Marketplace Sign-Ups and Simplifies Multi-Platform Access
Read story

Hongkong Land adopted Authgear to meet strict security requirements with zero trust authentication, while enabling seamless access for both staff and agents. This reduced IT workload and secured mobile-ready login across user groups.
Read story
MTR Corporation streamlined access to its part-time job platform with Authgear — integrating Azure AD for station managers and WhatsApp OTP for part-time staff. Resulting in stronger security, simpler access, and reduced IT overhead.
Read story
Bupa enhanced login security and usability with Authgear by implementing biometric authentication in mobile apps
Read story
Global F&B leader
One of the world's largest fast-food chains adopted Authgear to meet strict global security standards with 2FA and SSO — all while delivering a user-friendly, biometric login experience for back-office & frontline staff. The result: faster access and fewer support issues.
Read story
Security shouldn't slow you down.
Ship a production login this week.
What you get out of the box, and what you would otherwise be building and maintaining yourself.

Customizable login page
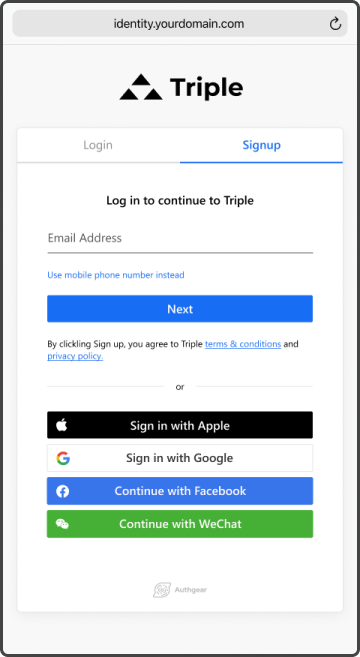
Pixel-perfect UIs in minutes.Hosted login with passkeys, social login and MFA already wired up, live on your own domain. Brand it in the portal, or customize the UI with AI agents.

Every modern login method
Passkeys, biometrics, and WhatsApp OTP.SMS OTP, magic links, and social login too.
For enterprise: SAML, Microsoft Entra ID, Active Directory, and LDAP.
Each one is a setting, not an integration.
For enterprise: SAML, Microsoft Entra ID, Active Directory, and LDAP.
Each one is a setting, not an integration.

Hooks and Admin API for your rules
Customize every rule with TypeScript.Gate signups by IP or domain, add claims at token issuance, validate profiles before they save, fire webhooks into your CRM. Everything the portal does, the Admin API does.

Native SDKs
Swift, Kotlin, Flutter, React Native, and web SDKs.Users stay in your app instead of bouncing out to a browser. Sessions, token refresh, and biometric unlock are built in, so you add one dependency instead of writing an auth layer.

Design your flows without code
Visual editor to design your flows.Add a profile field, insert a verification step, or reorder the whole journey, then publish without a deploy. Give each app its own flow, so a consumer signup and a frontline onboarding can look nothing alike.
Secure every user journey with
Authgear's tailored solutions
Authgear delivers robust IAM solutions designed to meet the specific needs of your business.
Customer identity
Consumers who abandon at friction. Passkeys and social login instead of passwords, WhatsApp or SMS OTP where email doesn't reach, and single sign-on across your apps so one customer stays one profile everywhere they appear.
Extended workforce
Frontline and deskless staff, contractors and partners. Phone-number login for people with no corporate email, batch user creation and groups for shift turnover, and ADFS or Google Workspace for office staff.
B2B SaaS apps
Business customers who bring their own identity provider. SAML SSO and Microsoft Entra ID on every plan, plus roles and groups so each tenant administers its own users.
One identity across
every app you run
One sign-in for a dozen microservices or a whole product portfolio. Every service trusts the same token.
One login, every service
Connect OIDC once and every app you operate trusts the same identity provider: web, mobile, internal tools, partner portals. The next app is a config change, not another auth integration.
One customer record, every touchpoint
One identity per person across mobile, web, and partner portals. Profiles, roles and entitlements update once and apply everywhere. Every login lands in one audit log.
Move between apps, stay signed in
App-to-app and app-to-web SSO hand an authenticated session from your mobile app straight into your web portal or your next app. No second login and no drop-off at the handoff.
Auth for AI agents and MCP servers
Put Authgear in front of your MCP server as its OAuth authorization server. Agents register through CIMD or Dynamic Client Registration. Users grant scopes on a consent screen, so an agent never gets more than the user has, or more than the user approved.
Build a zero-trust foundation
Authgear aligns with zero-trust principles by enforcing "never trust, always verify" for every request.
Stolen tokens stop working
Sender-constraining with OAuth DPoP binds every refresh token to a key on the device that requested it. Lift the token off that device and it won't work.
Re-check before risky actions
Re-authenticate users for sensitive actions: require a fresh passkey, TOTP or OTP before a transfer, permission change or account deletion.
Bot and fraud protection
Bot protection puts CAPTCHA on signup, login and password reset via reCAPTCHA or Turnstile. Fraud detection watches OTP patterns by IP and country, observing or blocking live.